Breaking the Judicial Umbilical Cord: Digital Nomad Anti-Phishing Defense and Hardware Isolation
Debunking the illusion that changing your IP guarantees safety. Cross-border enforcement doesn't rely on elite hacking, but on local meetups, OTC black money, and targeted phishing. Discover the 'gas chamber' dual-device strategy and absolute data decoupling.

Executive Summary: In an era of mature, ubiquitous digital surveillance, digital nomads who imagine that simple “geographical arbitrage” cuts their umbilical cord to domestic oversight are operating under a fatal cognitive illusion. In reality, network phishing and law enforcement stings do not rely on cutting-edge zero-day exploits. Instead, they weaponize convenience, artificial echo chambers, tainted OTC funds, and device telemetry to achieve precise doxxing and inbound capture at minimal cost. Facing multidimensional digital sniffing, the only definitive defense for high-frequency cross-border netizens to preserve personal freedom and border-crossing safety is the strict application of a Zero Trust architecture: deploying a dedicated “gas chamber” burner device for absolute physical hardware isolation, severing all return channels for identity and capital, and refusing to become uncompensated rhetorical fodder.
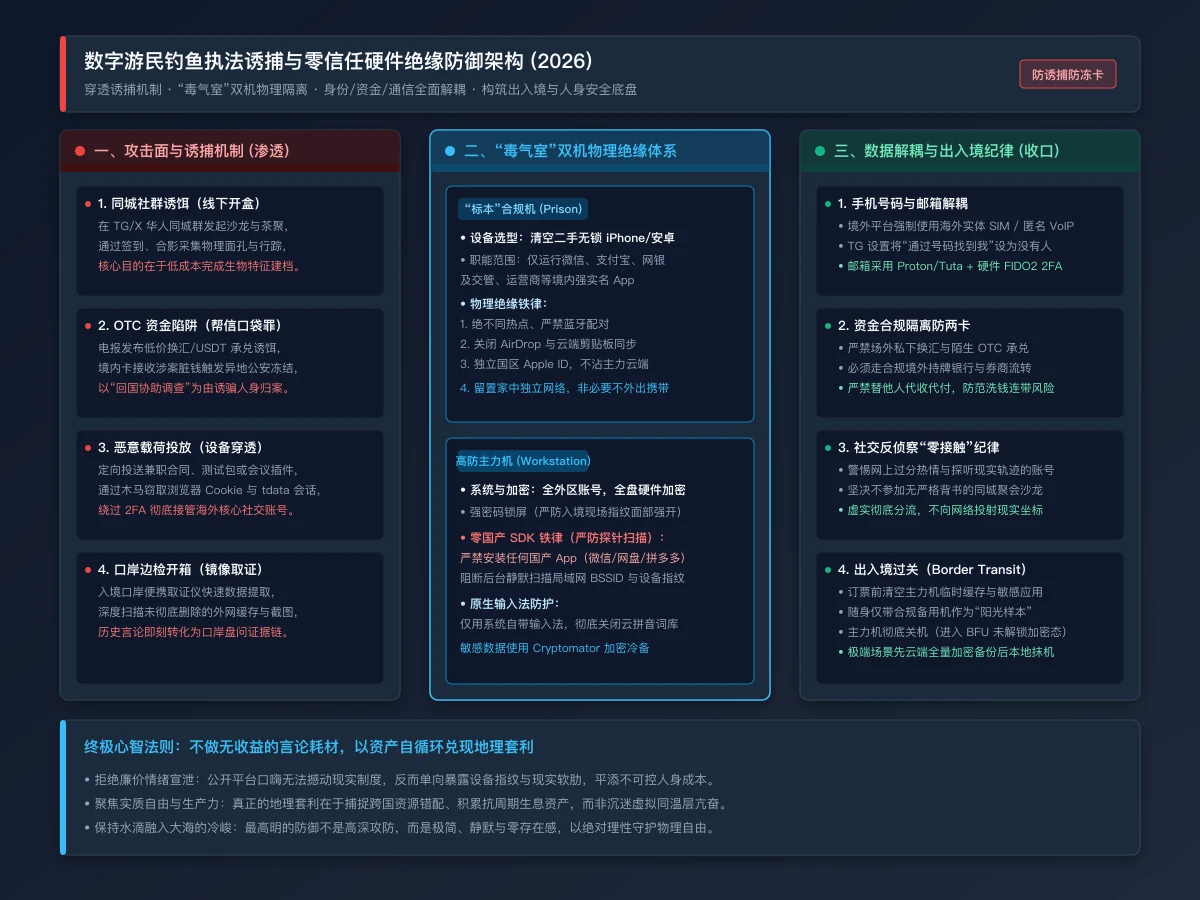
Figure 1: The Digital Nomad Phishing Trap, Dual-Device Hardware Isolation, and Zero Trust Defense Architecture. Through physical isolation via “gas chamber” devices and a zero-domestic-SDK policy, exposure to domestic telemetry and port-side mirroring forensics is thoroughly neutralized.
Evidence Chain Comparison: Nomad Blind Spots vs. Real-World Stings and Defense Benchmarks
Many netizens assume that once they cross a national border or transition to remote work, purchasing a commercial VPN or a foreign native SIM card grants absolute immunity. In actual judicial practice and intelligence reconnaissance logic, however, the security chain is consistently breached through the most vulnerable details of everyday life:
| Attack Surface / Scenario | Surface Reality: Common Misconceptions (Cosmetic Defenses) | The Dark Line: Actual Stings and Judicial Evidence | Hardcore Zero Trust Countermeasures |
|---|---|---|---|
| Local Social Meetups | Overseas offline gatherings are private, safe spaces for mutual expat support. | Undercover operatives infiltrate meetups, logging facial biometrics and physical trajectories via check-ins and group photos. | Anti-Echo Chamber Policy: Strictly bifurcate real and virtual lives; never attend unvetted local networking events. |
| P2P Currency Exchange | Telegram OTC trades offer favorable rates and instant transfers without platform oversight. | Illicit funds injected into domestic accounts trigger cross-border freezes, leading to “voluntary return” stings. | Hard Isolation of Financial Channels: Use only licensed overseas banks and regulated brokerages; strictly ban peer-to-peer OTC. |
| Remote Recruitment & Gigs | Employment contracts, test task packages, and meeting links from foreign firms are harmless. | Targeted macros or trojans deployed to steal browser cookies and Telegram tdata. | Payload Sandbox Isolation: Parse all unknown attachments exclusively inside virtual machines or isolated environments. |
| Domestic Real-Name Apps | As long as the primary device runs the latest iOS/Android, domestic apps cannot overreach. | Domestic SDKs continuously scan local Wi-Fi BSSIDs, peripheral fingerprints, and the clipboard. | “Gas Chamber” Burner Isolation: Isolate WeChat and online banking entirely on a secondary, secondhand burner device. |
| Border Customs Inspection | Logging out of overseas social accounts makes you invisible to border inspection. | Portable forensic tools extract full device mirrors in seconds; unsaved caches and deleted photos are recovered. | BFU Shutdown or Secure Wipe: Power down into the encrypted Before-First-Unlock state, or wipe the device entirely after cloud backups. |
I. Piercing the Illusion: The Real Mechanics of Phishing Enforcement
Long-term judicial practice in cyber-governance and target profiling has evolved into a highly engineered pipeline: Low-cost forensics -> Interest/Empathy manipulation -> Physical geolocation and inbound capture. Law enforcement and intelligence personnel understand that cracking end-to-end encryption (such as Signal or Telegram private chats) is technically prohibitive. Consequently, they bypass robust encryption protocols entirely to strike at your most unguarded flanks.
Common entrapment vectors cluster heavily around four blind spots:
1. Local and Community Decoys (Offline Interception)
Within overseas Chinese-language Telegram, Signal, or X groups and nomad clubs, undercover operatives frequently organize offline events disguised as “freelancer tech salons,” “Web3 offline tea sessions,” or “overseas mutual aid forums.”
- Low-Cost Doxxing: The primary objective is rarely immediate physical enforcement abroad. Instead, it exploits your psychological need to integrate into an echo chamber. Through sign-in registries, group photos, and splitting bills via QR codes, they effortlessly harvest the real facial biometrics, device Wi-Fi MAC addresses, and physical locations of everyone present, directly linking and anchoring these to domestic household registries.
2. Financial and OTC Traps (Judicial Entrapment)
The vast majority of overseas freelancers face the practical reality of cross-border cash flow and currency exchange. Phishing operators understand this pain point, frequently posting “favorable exchange rates” and “USDT cash escrow” offers across major communities.
- Complicity Traps: Once your domestic bank account receives tainted funds transferred by a counterparty, domestic anti-fraud systems and economic crime investigation units will trigger an emergency inter-provincial freeze within hours.
- Coerced Summons: Investigative officers subsequently cite “suspicion of aiding cybercrime” or “concealing criminal proceeds,” contacting you via your local police station or direct phone call to demand your “return within a set deadline to assist with the investigation and unfreeze assets,” thereby tricking the target into actively re-entering the jurisdiction.
3. Malicious Payloads and Targeted Phishing (Device Penetration)
For individuals with technical competence or industry influence, phishing methodologies are disguised with extreme professionalism.
- Specialized Payload Delivery: Attackers impersonate overseas HR managers or recruiters, sending direct messages with “remote development employment contracts,” “freelance specifications” (disguised as
.scr,.exe, or macro-embedded.docmfiles), or prompting you to download standalone encrypted video conferencing clients. - Credential Stealers: Upon execution, malware silently packages and uploads all browser-stored cookies, password credentials, and Telegram local session keys (
tdata) within seconds, enabling seamless hijacking of entire account suites without requiring SMS verification codes.
4. Physical Inspection and Mirroring at Border Crossings
For optimistic netizens, the most fatal point of failure occurs at international border checkpoints.
- Portable Forensic Extraction: No matter how meticulously you scrub your online footprint abroad, if you cross the border carrying your primary device, customs officials possess the legal authority to require device unlocking. Portable digital forensics workstations deployed at ports can perform read-only image extractions of mobile devices in mere minutes.
- Fragment Reconstruction: Unoverwritten SQLite database caches, instant messaging thumbnail caches, photo histories, and metadata from deleted files are exposed under deep forensic scans, serving as definitive written evidence for on-site detention and interrogation.
II. The Iron Law of Hardware Isolation: Building the “Gas Chamber” Burner System
Software-layer privacy settings remain fragile against OS kernel vulnerabilities, permission abuses, and domestic hardware backdoors. In digital defense, the simplest and most unbreakable axiom is absolute physical hardware isolation. High-frequency netizens must abandon the illusion of running multi-role operations on a single device, adopting a strictly stratified dual-device architecture instead:
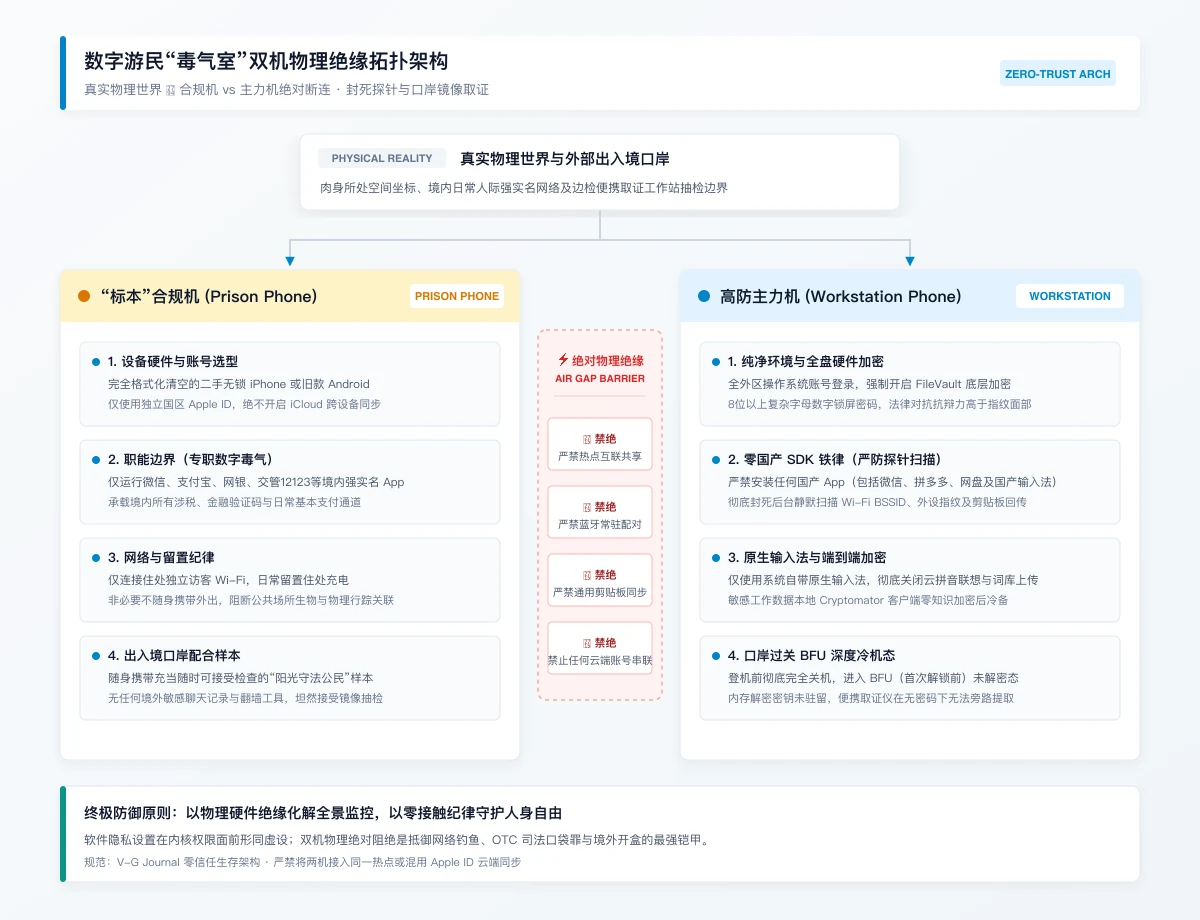
Figure 2: Absolute physical isolation architecture between the physical world and digital survival. On the left sits the compliant “specimen” phone dedicated to domestic real-name apps; on the right is the hardened primary workstation phone with full-disk hardware encryption. The two devices remain 100% physically decoupled across an air gap regarding hotspots, Bluetooth, clipboards, and account ecosystems.
| Isolation Dimension | 📱 Compliant “Specimen” Phone (Prison Phone) | 🛡️ Hardened Workstation Phone (Workstation Phone) | Physical Isolation & Interaction Boundary |
|---|---|---|---|
| Hardware & Selection | Completely wiped secondhand, unlocked iPhone or legacy Android device | Flagship hardware with underlying full-disk hardware encryption enabled | Physical Disconnection: Dual devices feature independent power supplies and storage; hardware cores are never shared. |
| Accounts & Environment | Logged into an independent domestic Apple ID / stock factory firmware only | Global-region native system accounts only; high-entropy lock screen passwords (8+ chars) | Zero Trust Account Chains: Cross-device cloud backups, photo sharing, and keychains are strictly prohibited. |
| Business Scope | Dedicated “Digital Gas Chamber”: Runs only domestic real-name apps like WeChat, Alipay, online banking, etc. | Pure Productivity: Runs overseas work tools, Telegram, password managers, offshore banking, and core projects | Zero Domestic SDK Rule: Installing domestic apps on the workstation is strictly forbidden to block background telemetry scanning. |
| Network & Connectivity | Connects exclusively to residential guest Wi-Fi; remains at home and is rarely carried out | Dedicated encrypted channel with firewall and encrypted DNS permanently enabled | Absolute Non-Interconnection: Hotspot sharing, Bluetooth pairing, and AirDrop discovery are strictly forbidden. |
| Clipboard & Data Flow | Cloud clipboard completely disabled; copying sensitive text is strictly prohibited | System-native input methods only; cloud predictive input dictionaries completely disabled | No Cross-Device Bridging: Sensitive credentials must never be copied and pasted directly between devices. |
| Border Crossing Defense | Carried as a compliant “sunny citizen” specimen to undergo routine random checks | Powered down completely into the BFU (Before First Unlock) unencrypted state, or locally wiped beforehand | Block Forensic Mirroring: Portable forensic tools cannot bypass and extract BFU memory encryption keys without the password. |
1. Establish a Dedicated “Compliant Specimen” Burner (Prison Phone)
Quarantine all “digital gas” applications—those you cannot shed but which deeply bind your domestic social relationships and financial assets—into a dedicated isolation cage:
- Device Selection: A fully formatted, wiped secondhand unlocked iPhone (e.g., iPhone 11/12) or a legacy Android device with factory firmware restored.
- Scope of Function: Used exclusively and solely for running domestic real-name apps (WeChat, Alipay, banking apps, transit utilities, domestic airline clients, and telecom apps).
- Four Iron Rules of Physical Isolation:
- No Hotspots, No Bluetooth: Personal hotspot sharing between the burner and workstation is strictly forbidden; Bluetooth must remain physically disabled to prevent local network topology discovery.
- No Shared Clipboard or AirDrop: Never use AirDrop or multi-device clipboard sync tools between the devices, preventing sensitive text from leaking via accidental copy actions.
- No Associated Cloud Accounts: The burner uses an exclusively registered domestic Apple ID, completely isolated from any iCloud backups, photo sharing, or keychain syncing with the workstation’s primary foreign account.
- Not Carried Routinely: The device remains at home connected to an independent guest network. Except for daily consumer payments or receiving critical SMS verification codes, it is never carried into public social settings.
2. Build the Hardened Workstation Phone (Workstation Phone)
The workstation phone is the sanctuary carrying your cross-border livelihood, core asset private keys, and private mental space. It must remain uncompromisingly pure:
- Pristine OS and Full-Disk Encryption: Logged in exclusively via overseas native operating system accounts, with full hardware disk encryption forced at the kernel level (iOS hardware protection / Android FileVault-equivalent). Set an alphanumeric lock screen password of 8 characters or more (Remember: under legal confrontation and border coercion scenarios, numeric passwords hold vastly superior legal defense protections compared to biometric fingerprints or facial recognition).
- Zero Domestic SDK Rule: Installing any domestic apps (including WeChat, Pinduoduo, Baidu Netdisk, third-party input methods, or domestic browsers) on the workstation phone is strictly prohibited. The aggressive telemetry and persistent background tracking embedded in mainstream domestic software are fully capable of scanning your connected Wi-Fi’s BSSID (the unique physical identifier of wireless access points, enabling meter-level geolocation), local network device lists, and system clipboard histories.
III. Identity and Data Decoupling: Severing the Digital Umbilical Cord
If hardware is the container, data flow is the cable. Many netizens implement physical hardware defenses while voluntarily handing the reins to surveillance systems via their basic communication data chains. Comprehensive zero-trust decoupling must be established at the communication foundation:
1. Phone Numbers: Severing Real-Name Mappings
- High-Risk Behavior: Registering Telegram, X, Signal, or core Google accounts directly using a
+86mobile number bound to WeChat, Alipay, or domestic bank accounts. - Zero Trust Guidelines:
- Overseas platforms must be registered exclusively using foreign native physical SIM cards (e.g., UK giffgaff, US Ultra Mobile) or anonymous VoIP numbers (e.g., Google Voice);
- Within Telegram privacy settings, force “Who can find me by my phone number” to Nobody, and enable local two-step verification (2FA) cloud passwords;
- Domestic
+86numbers remain exclusively on the burner phone to passively receive banking and government verification codes. Using them as contact channels in any public online context is strictly forbidden.
2. Financial Channels: Eliminating Tainted Funds and Judicial Entrapment
- High-Risk Behavior: Engaging in private fiat cash exchanges with self-proclaimed “compatriots” or “crypto peers” found in Telegram or WeChat groups, or conducting unverified OTC trades for slight exchange-rate spreads.
- Zero Trust Guidelines:
- Completely sever all private offline currency exchanges. All cross-border asset allocation must flow through compliant, licensed overseas commercial banks (such as Wise, or mainstream offshore banks in Singapore, Hong Kong, Europe, and the US) or regulated online brokerages.
- Resolutely refuse to receive or transfer funds on behalf of any real-world or online “friends,” preventing yourself from becoming a scapegoat and joint-liability target in a money-laundering chain.
3. Email Systems: Preventing Plaintext Email Penetration
- High-Risk Behavior: Using QQ or 163 email accounts to register for critical overseas services, cloud server management panels, or foreign social platforms.
- Zero Trust Guidelines:
- Domestic email services maintain comprehensive static content scanning, sensitive keyword interception, and judicial cooperation mechanisms. For any overseas business or sensitive account, you must mandate the use of ProtonMail, Tuta, or completely independent overseas Gmail accounts.
- Core mailboxes must enforce FIDO2-compliant physical hardware security keys (such as YubiKey), blocking man-in-the-middle phishing and session token hijacking at the hardware layer.
4. Input Methods and Storage: Blocking Side-Channel Keylogging
- High-Risk Behavior: Installing connected input methods like Sogou, Baidu, or iFlytek on your primary development machine or phone; using domestic commercial cloud storage for code repositories, journals, and sensitive documents.
- Zero Trust Guidelines:
- Workstation devices must use system-native keyboards only, with “cloud pinyin,” “predictive cloud dictionaries,” and “input improvement programs” completely disabled in system settings.
- Sensitive work data must undergo client-side, zero-knowledge end-to-end encryption using open-source tools (such as Cryptomator or VeraCrypt) locally before syncing to secure cloud storage or offline cold storage media.
IV. Social Defense Principles: Counter-Reconnaissance and “Zero-Contact” Discipline
In real-world social engineering offense and defense, humans remain the most vulnerable node in any system. Establishing a counter-intuitive, cold discipline of social conduct is the core firewall against targeted entrapment:
1. Beware of Over-Enthusiastic and Probing Accounts Online
Any account that actively initiates private chats on social networks, expresses extreme admiration and resonance with your rhetoric, and subsequently probes for the following information should be immediately classified as high-risk, muted, and blocked:
- Frequently asking for your current physical city, housing type, or the co-working spaces and cafes you frequent.
- Inquiring about your upcoming border-crossing schedules, passport renewal locations, or family visit plans.
- Strangers in your industry proactively offering “high-paying project interviews” or suggesting to “drop by for a drink.” In the absence of multi-year backing from multiple trusted real-world friends, online identities must never intersect with offline physical trajectories.
2. Adhere Strictly to the “Anti-Echo Chamber Meetup” Principle
Never attend offline networking events, overseas political salons, or sensitive micro-circle seminars organized by Telegram local city groups or unvetted social circles. Many newcomers abroad experience an illusory sense of “liberation” upon leaving their home country, seeking intense validation and expressive compensation among expat communities. You must recognize clearly: True nomadism and geographical arbitrage are about inward exploration and personal self-sovereignty, not jumping from one collective domestic conditioning into another hazardous, virtual echo-chamber fervor.
3. Extreme Operational Protocols for Border Transit
During sensitive moments crossing national borders, all security policies must shift to the highest alert level:
- Advance Data Sanitization: More than 48 hours before booking return flights, thoroughly uninstall and clean all non-essential social software, sensitive group chat histories, and browser search trails from your workstation device.
- Dual-Device Physical Stratification: Keep the burner device (containing only compliant everyday apps) easily accessible in an outer pocket, serving as the “model sunny citizen” specimen ready for routine security inspection.
- Cold Encryption (BFU State): If your workstation must cross the border with you, power it down completely before boarding. In modern mobile operating systems, powered-down devices enter the BFU (Before First Unlock) state. The filesystem remains fully encrypted, and decryption keys do not reside in memory. Even specialized port-side forensic tools cannot perform side-channel physical data extraction without the device password. If extreme legal exposure risks exist, back up all local data encrypted to an overseas server beforehand, factory-reset the workstation locally into a blank device, and remotely restore data only after arriving safely abroad and settling down.
V. Ultimate Mindset: Refusing to Be Uncompensated Rhetorical Fuel
The highest dimension of risk management never relies on esoteric hacker counter-attacks, but on absolute clarity regarding your own interest-alignment boundaries:
- Reject Blind, Public Emotional Venting: Hammering keyboards on public social platforms to vent anger neither alters the gears of massive institutional machinery nor adds a single penny to your offshore bank accounts. Instead, such cheap emotional release uniquely exposes your linguistic fingerprints and digital profile, adding amplified and entirely uncontrollable legal costs to your future border crossings, asset dispositions, and family well-being back home.
- Channel Strategic Focus into “Substantive Freedom”: The core of true geographical arbitrage, modern FIRE (Financial Independence, Retire Early), and the digital nomad ethos lies in keenly capturing global resource mismatches—lawfully deploying productivity in tax-friendly, rule-of-law jurisdictions, enjoying sunshine and nature in low-cost-of-living regions, and building anti-fragile survival resilience through self-sustaining offshore asset loops.
Allow your digital footprint to dissolve into the sea like a drop of water. Remaining silent, minimalist, and highly professional amidst the torrent of the internet is the strongest armor against the turbulent waves of our era.
Related Research & Topics
Starlink V4 and the Low-Earth Orbit Satellite Arms Race: How a 100,000-Node Optical Mesh Pierces the Submarine Cable Monopoly
The Cyprus Pension Overhaul of 2027: Nomad Social Security Traps and Offshore Asset Defense
Tello Mobile eSIM
SafetyWing Nomad Insurance
* Disclosure: This post contains affiliate links. If you make a purchase through these links, V-G Journal may earn a small commission at no additional cost to you. We only recommend services we independently evaluate and trust.
FIRE and Golf:自由旅居之路
专注于为追求 FIRE 与品质生活的人群提供特惠打球权益与候鸟微度假。不持一砖一瓦,运营品质生活。